Provider
MASKIFY
- Website
maskify[.]su
- Events · 24 hours
- Locked
- Events · 7 days
- Locked
- Unique IPs · 7 days
- Locked
- /24 subnets · 7 days
- Locked
- Countries · 7 days
- Locked
- ASNs · 7 days
- Locked
Live provider metrics are available with full access.
Provider overview
Maskify is a Russia-oriented proxy service operating since 2025, known for no-KYC token accounts, cryptocurrency payments, residential proxies, and white-label services. It is considered medium sized. Synthient has identified BudgetProxy, VaultProxies, qProxy, and SousMarket as resellers. These indirect channels and absent customer KYC create abuse and accountability risk.
Maskify is observed leveraging Earnify on Android. Earnify is classified as Malware and has been observed in Ambient Display Core and Android system-service packages. January 2026 research separately identifies Maskify as a sales route for Kimwolf-associated proxies; this does not establish that Earnify and Kimwolf are the same family or that every exit was infected.
Synthient's Research Team assigns a HIGH risk score to Earnify based on a randomized sample of consent practices observed in the wild. Sampled packages used system-service names, persistence, and native payload replacement without a clear bandwidth-sharing consent or reward flow.
Provider relationships
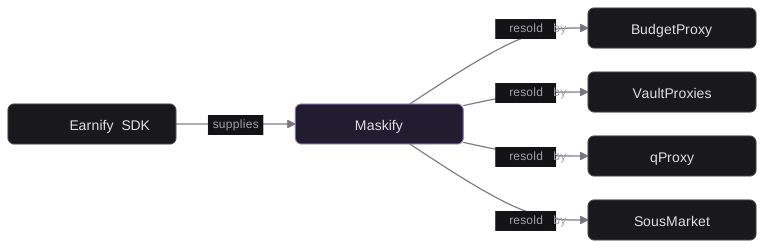
Yara Rules
rule Proxyware_Earnify_Android_NativeSDK
{
    meta:
        description = "Earnify/Maskify Android Rust/QUIC proxy SDK"
        provider    = "Maskify"
        sdk         = "Earnify"
        category    = "proxyware"
        author      = "Synthient"
        date        = "2026-08-31"
        confidence  = "high"
        platform    = "android"
        variant     = "native-sdk"
        intel_family = "earnify"
    strings:
        $jni_1 = "Java_io_earnify_sdk_EarnifySDK_nativeInit" ascii fullword
        $jni_2 = "Java_io_earnify_sdk_EarnifySDK_nativeStart" ascii fullword
        $jni_3 = "Java_io_earnify_sdk_EarnifySDK_nativeGetBytesProxied" ascii fullword
        $abi_1 = "earnify_sdk_init" ascii fullword
        $abi_2 = "earnify_sdk_start" ascii fullword
        $abi_3 = "earnify_sdk_stats" ascii fullword
        $abi_4 = "earnify_sdk_set_consent" ascii fullword
        $session_1 = "expected control stream from server" ascii
        $session_2 = "expected ConnectToServer" ascii
        $session_3 = "relayserver did not assign client_id" ascii
        $session_4 = "session auth rejected" ascii
        $mesh_1 = "peer exchange: truncated node_id" ascii
        $mesh_2 = "no resolver set for this ENS name" ascii
        $mesh_3 = "IPFS seed resolution not yet implemented" ascii
        $mesh_4 = "Za Rodinu mesh config found" ascii
        $relay_1 = "earnify-core/src/tunnel.rs" ascii
        $relay_2 = "TCP connected, relaying" ascii
        $relay_3 = "UDP connected, relaying" ascii
        $relay_4 = "received ConnectToServer signal" ascii
    condition:
        uint32(0) == 0x464c457f and filesize > 1MB and filesize < 5MB and
        2 of ($jni_*) and 3 of ($abi_*) and 2 of ($session_*) and
        (2 of ($mesh_*) or all of ($relay_*))
}
This rule identifies an SDK family. A match alone does not establish malicious activity or the absence of consent.
Indicators of Compromise
File Hashes
- Type
- SHA-256
- Context
- Unstripped Earnify Rust/QUIC native SDK
- Type
- SHA-256
- Context
- Stripped Android Earnify SDK
- Type
- SHA-256
- Context
- Earnify Android native library version 1.0.0
- Type
- SHA-256
- Context
- Earnify Android native library version 3.1.0
- Type
- SHA-256
- Context
com.android.server.ambientAPK
- Type
- SHA-256
- Context
- Earnify Android loader DEX
- Type
- SHA-256
- Context
- Guardian downloader and launcher DEX
- Type
- SHA-256
- Context
- Persistent guardian ELF
- Type
- SHA-256
- Context
- Confirmed files; Earnify
- Type
- SHA-256
- Context
- Confirmed files; Earnify
Domains
- Type
- Domain
- Indicator
- Context
- Commercial proxy provider
- Type
- Domain
- Indicator
- Context
- Declared bandwidth-sharing network
- Type
- Domain
- Context
- Earnify update and fallback service
- Type
- Domain
- Context
- Shared gateway alias used by Maskify, BudgetProxy, and VaultProxies
- Type
- Domain
- Indicator
- Context
- BudgetProxy gateway sharing the Maskify alias and three rotated IPs
- Type
- Domain
- Indicator
- Context
- ENS dead-drop used for server and update discovery
- Type
- Domain
- Indicator
- Context
- VaultProxies gateway sharing the Maskify alias and four rotated IPs
- Type
- Domain
- Indicator
- Context
- qProxy gateway sharing four Maskify gateway IPs
- Type
- Domain
- Indicator
- Context
- Historical direct CNAME to
resi.maskify.su
IP Addresses
- Type
- IP address
- Indicator
- Context
- Current
resi.maskify.sugateway observed by VirusTotal
- Type
- IP address
- Indicator
- Context
- Rotated Maskify gateway
- Type
- IP address
- Indicator
- Context
- Maskify, VaultProxies, and qProxy gateway overlap
- Type
- IP address
- Indicator
- Context
- Maskify, VaultProxies, qProxy, and SousMarket gateway overlap
- Type
- IP address
- Indicator
- Context
- Maskify, VaultProxies, qProxy, and SousMarket gateway overlap
- Type
- IP address
- Indicator
- Context
- Maskify and BudgetProxy gateway overlap
- Type
- IP address
- Indicator
- Context
- Maskify, BudgetProxy, VaultProxies, qProxy, and SousMarket gateway overlap
- Type
- IP address
- Indicator
- Context
- Historical Maskify gateway; shared hosting, not reseller evidence
- Type
- IP address
- Indicator
- Context
- Historical Maskify gateway shared by BudgetProxy and other proxy storefronts
- Type
- IP address
- Indicator
- Context
- Historical Maskify gateway; shared hosting, not reseller evidence
Additional IOCs are hidden.
Available to subscribers. This preview shows up to ten IP addresses, ten domains, and ten file hashes.
Events & unique IPs
Hourly · 7 days · UTC
Illustrative preview
See the activity behind the provider.
Unlock daily events and unique IP trends to understand how this provider’s network changes over time.