PROXYBOX
Provider- Website
proxybox[.]com
ProxyBox was a residential proxy service of unverified jurisdiction, described in March 2026 research as the successor to PROXY.AM after its 2024 disruption. ProxyBox was seized after publication of Synthient's research. It sold access to Socks5Systemz-compromised devices. Synthient observed 32,000–35,000 daily active IPs at publication; no size tier or named downstream reseller was established. IP overlap suggested possible onward sales with moderate confidence, not a confirmed reseller list.
ProxyBox was observed leveraging Socks5Systemz on Windows. Socks5Systemz is Malware, distributed through cracked-software/PPI chains and a loader disguised as Game Backup Manager. The malware supplies residential proxy exits from infected devices.
Synthient's Research Team has not assigned a randomized SDK consent risk score to Socks5Systemz. The investigation documents malware-based compromise, not voluntary bandwidth sharing.
Reseller Graph
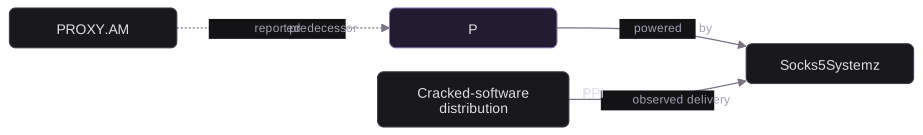
The highlighted node is the provider named on this card. Historical service continuity and malware-delivery edges are labeled separately; no unverified downstream reseller is shown.
Yara Rules
import "pe"

rule Proxyware_Socks5Systemz_Windows_Direct_Proxy_Core
{
    meta:
        description = "ProxyBox/Socks5Systemz final Windows proxy DLL, excluding installers and loaders"
        author      = "Synthient"
    strings:
        $telemetry = "gpt=%.8x&inc=%d&advizor=%d&box=%d&hp=%x&lp=%x&line=%d&os=%d.%d.%04d&flag=%d&itd=%d" ascii
        $user_agent = "Mozilla/5.0 (Windows; U; MSIE 9.0; Windows NT 9.0; en-US)" ascii
        $request = "/ai/?key=" ascii fullword

        $connect = "connect" ascii fullword
        $disconnect = "disconnect" ascii fullword
        $updips = "updips" ascii fullword
        $updurls = "updurls" ascii fullword
        $auth_typo = "auth_swith" ascii fullword
        $auth_ip = "auth_ip" ascii fullword

        $inet_open = "InternetOpenUrlA" ascii fullword
        $inet_read = "InternetReadFile" ascii fullword
        $socket = "WSASocketA" ascii fullword
        $recv = "WSARecv" ascii fullword
        $send = "WSASend" ascii fullword
    condition:
        uint16(0) == 0x5a4d and
        pe.machine == pe.MACHINE_I386 and pe.is_dll() and
        filesize > 550KB and filesize < 700KB and
        all of ($telemetry, $user_agent, $request, $auth_typo) and
        3 of ($connect, $disconnect, $updips, $updurls, $auth_ip) and
        4 of ($inet_open, $inet_read, $socket, $recv, $send)
}
Detects the final Windows proxy DLL, not every loader. The October 8 corpus review recorded matches against available reference files; a match does not establish current network activity.
Indicators of Compromise
Historical indicators from the March 2026 research; no current endpoint activity is asserted.
File Hashes
- Type
- SHA-256
- Context
- Gamemanager.exe loader
- Type
- SHA-256
- Context
- Second-stage loader
- Type
- SHA-256
- Context
- Socks5Systemz DLL
Domains
No malware domain indicator selected.
IP Addresses
- Type
- IP address
- Indicator
- Context
- Reported Tier 1 controller in March 2026; current activity unverified
- Type
- IP address
- Indicator
- Context
- Reported Tier 1 controller in March 2026; current activity unverified
- Type
- IP address
- Indicator
- Context
- Reported Tier 1 controller in March 2026; current activity unverified
Additional IOCs are hidden.
Available to subscribers. This preview shows up to ten IP addresses, ten domains, and ten file hashes.
7-day activity
Illustrative preview
See the activity behind the provider.
Unlock daily events and unique IP trends to understand how this provider’s network changes over time.